


Thank you for your cooperation and patience during Phase 1 of the multi-factor authentication rollout, which covered university systems. Across the entire university, our faculty achieved the best overall result, for which we owe you all a huge thank you. We would now like to ask for your cooperation once again in Phase 2:
Starting November 1, 2026 multi-factor authentication will be mandatory for signing in to faculty systems
The obligation to implement multi-factor authentication (MFA) stems from the Czech Cybersecurity Act. Nevertheless, let us view it as a positive step forward that significantly strengthens the protection of your account, your data, and the entire infrastructure. Please do not postpone setting up this service. If you need assistance, please contact the Helpdesk of the Information Technology Division FoS CU.
Set up multi-factor authentication for:
What specifically are faculty systems?
At the university, we use a range of systems shared with other faculties (e.g., SIS, Moodle). These were addressed during the first wave of the MFA rollout (using the CU Key app). In addition, at the Faculty of Science, we maintain our own systems used for work and study. These consist of two primary suites:
-
Google Workspace: This primarily concerns Gmail (login@natur.cuni.cz), but also applies to all applications across the Google ecosystem where you sign in with your faculty email. This includes tools such as the Gemini AI assistant and Google Drive.
-
Microsoft ecosystem: In this case, please note that users have access to two separate Microsoft environments (tenants) – either via university email (personal_number@cuni.cz) or via faculty email (login@natur.cuni.cz). While sign-in via your university email was already configured during Phase 1 (CU Key app), you must configure MFA again for access via your faculty email.
What does this mean for you?
- Your login will be significantly more secure. The procedure varies slightly depending on which method you choose:
-
Standard authentication: You log in with your username and password as usual, but you must also confirm the login with an additional step (e.g. in the mobile app) — similar to logging into online banking.
- Password-free login (passkey stored, for example, on a Yubikey hardware token or via Windows Hello): You no longer need to enter a password. You log in directly using a physical key, or a PIN, fingerprint or facial recognition.
-
-
Multi-factor authentication must be actively configured.
-
If you are a student, this measure is not yet mandatory for you. Nevertheless, we encourage you to enable MFA to protect your own data as well as faculty digital systems.
-
If you do not configure your second factor in time, you will not be able to access faculty Gmail, OneDrive, or MS Office 365.
-
Multiple sign-in factors can be configured. If you already have Google apps on your phone, you will barely notice the change.
-
Confirming your second factor is not something you will have to do multiple times a day. If you sign in from the same device, you will only be prompted from time to time. However, a sign-in from a new device will always require verification.
-
Please approach this measure as a routine part of a secure digital environment at Charles University and as a step in the right direction.
Why couldn't this be done all at once, in a single wave?
That was certainly an option. However, it came with significant drawbacks – both organizational and user-facing. Above all: at that time, it was not technically possible to sign in to the faculty Microsoft tenant using the CU Key app (as was done for university systems). Over the summer, a technical solution was achieved. If the rollout had taken place in a single wave, you would have had to download an additional application specifically for Microsoft. This is no longer necessary. We believe splitting this into two phases makes it easier to navigate, especially for less tech-savvy users. And rest assured, there are currently no further rollout waves planned.
What are the verification options?
-
CU Key: The app most of you downloaded to sign in to university systems. You can use it to sign in to faculty Microsoft services (OneDrive, Office 365).
-
Google prompt: If you have Google apps signed in with your faculty account on your smartphone, a notification prompt will pop up on your screen that you simply confirm. No extra downloads needed.
-
Hardware security key
-
Other available methods: Windows Hello, Microsoft Authenticator, Google Authenticator, Google Security Key
You must actively set up your chosen method. Detailed guides can be found below. To configure MFA, click here:
Cybersecurity starts with you!
Two-factor authentication is just one of the measures outlined in the Rector’s Directive; we recommend that you read it carefully. Above all, please follow the guidelines for safe online behavior, because security depends on all of us. A single lapse in judgment can provide an opening for hackers.
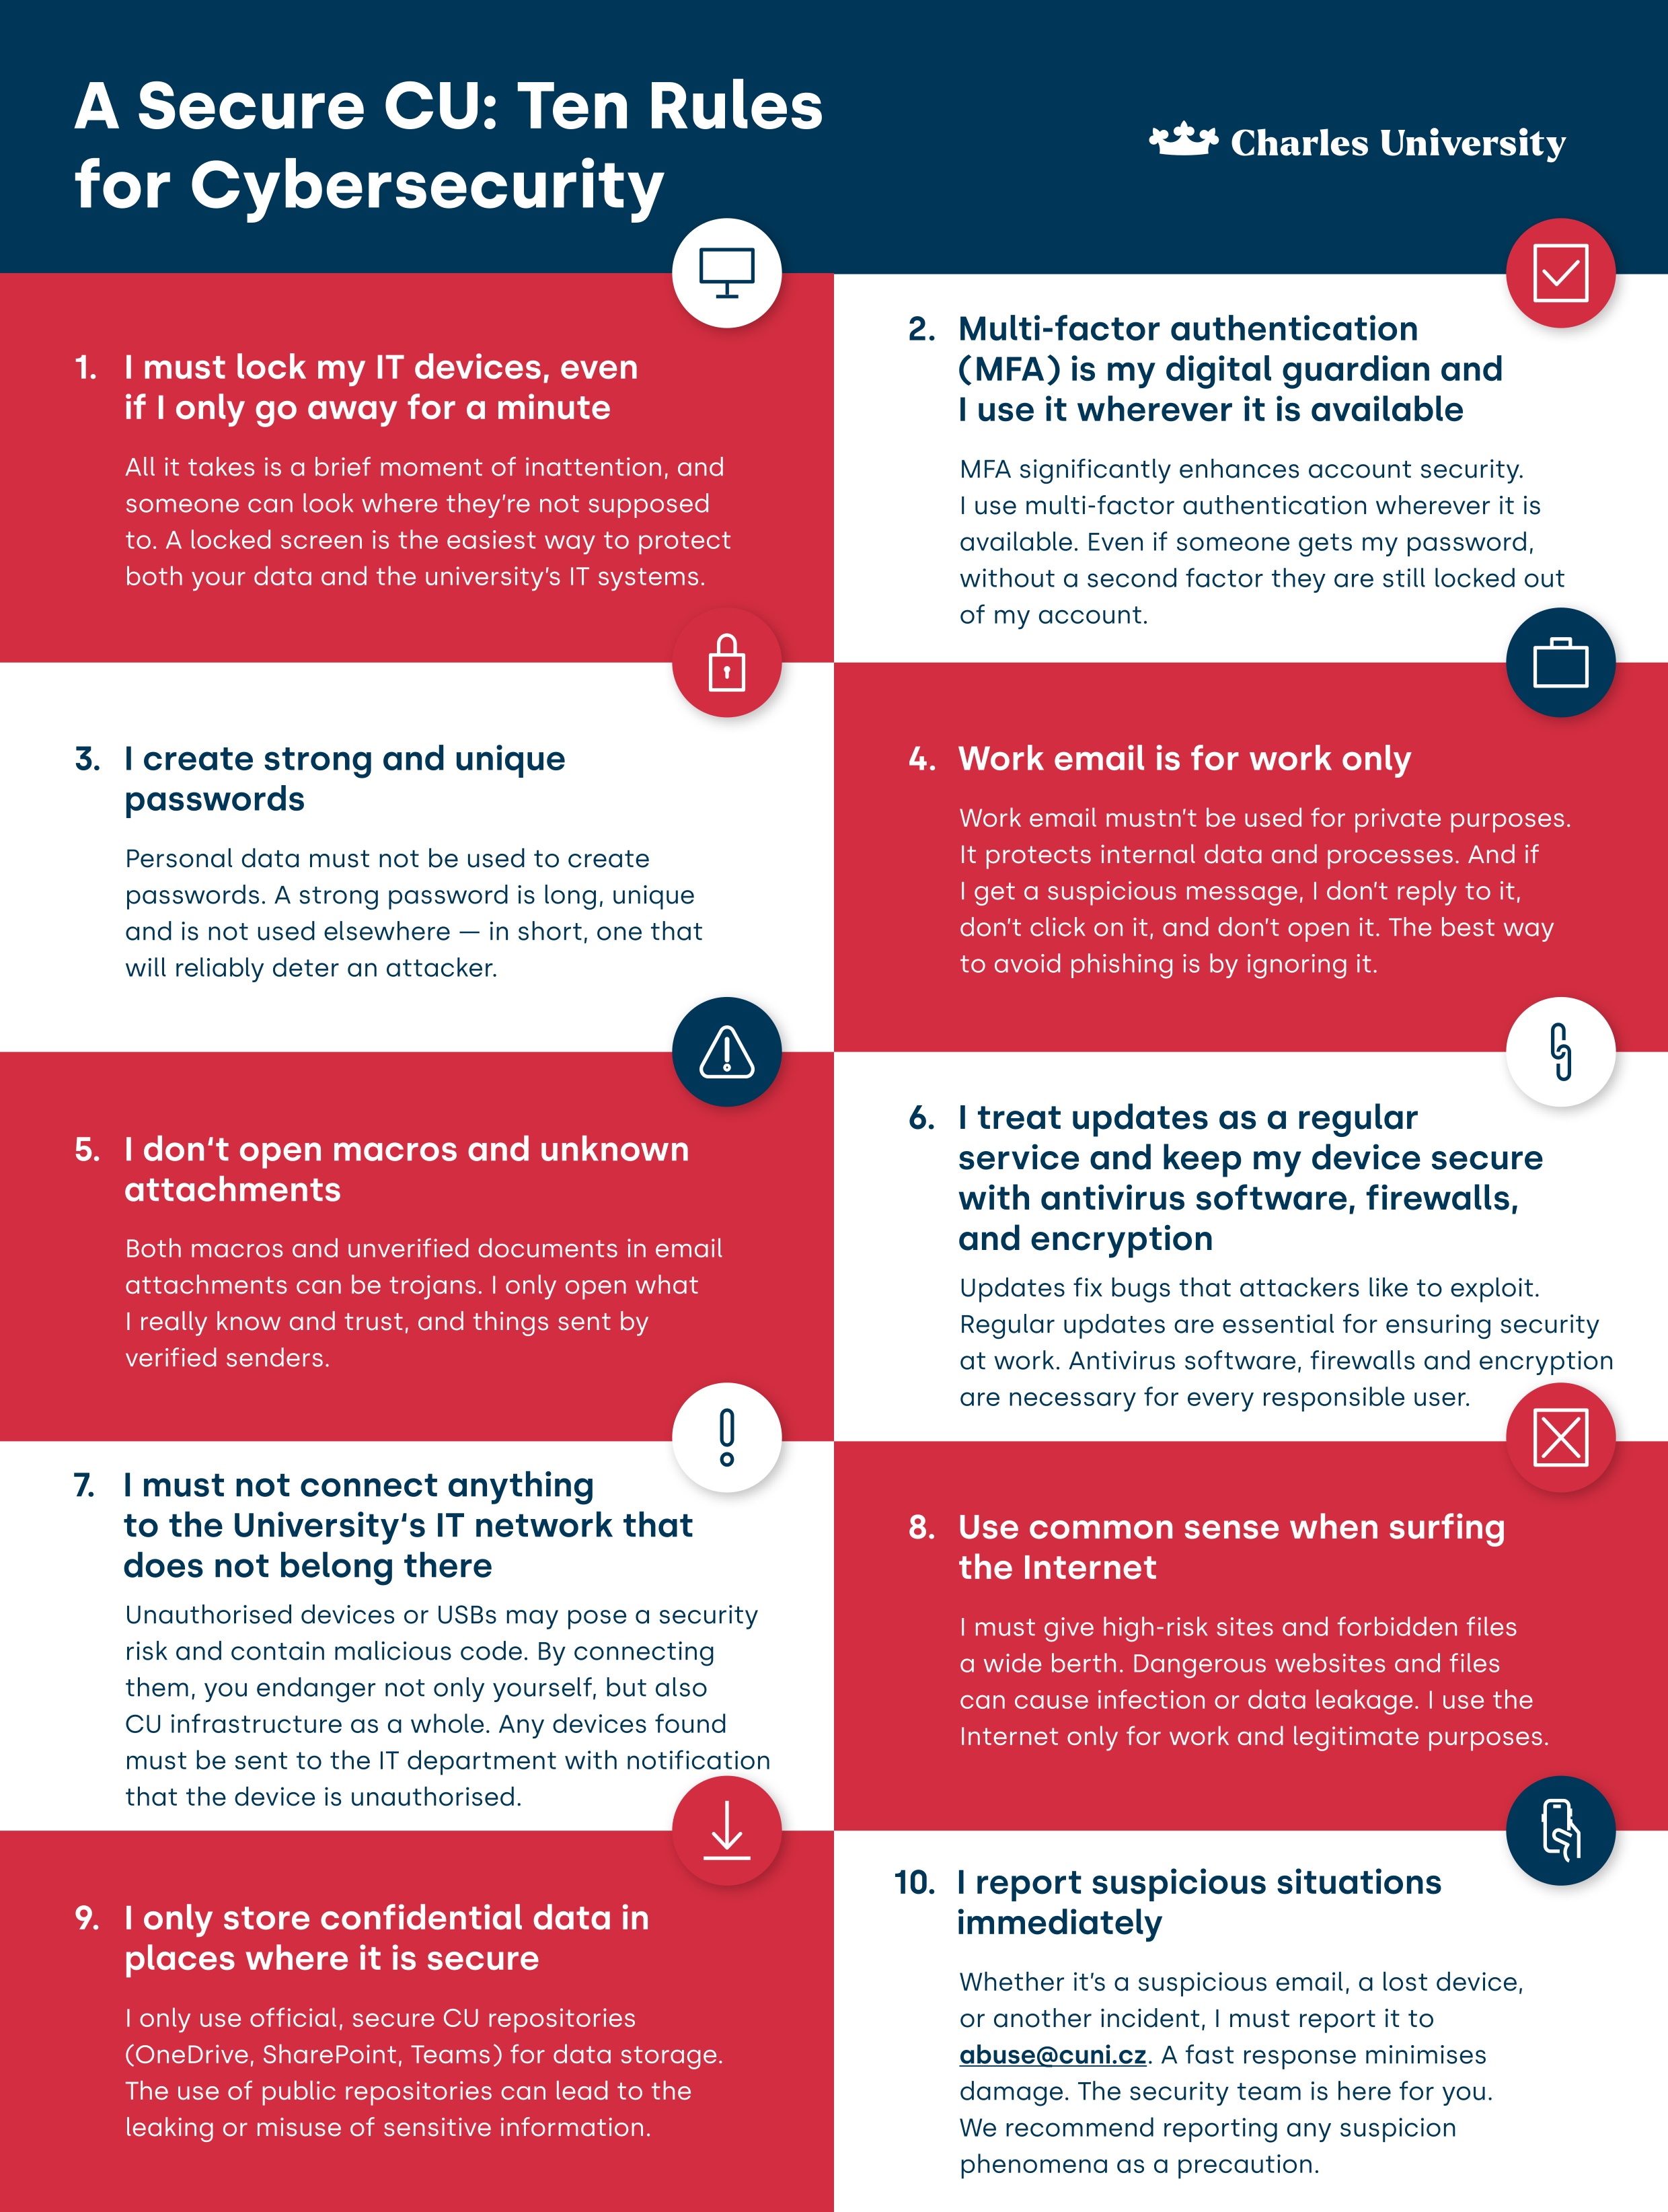
P.S. Two-factor authentication is an important part of cybersecurity. For further context, we recommend listening to the May episode of the faculty podcast Hello from the Dean!, which featured Dr. Jan Pačes, a member of the Rector’s Board for Institutional Resilience and Knowledge and Technology Transfer, as a guest. You can listen to the episode on Youtube.